
Two-Factor Authentication. Completely Zero-Knowledge.
FlincByte Authenticator generates RFC 6238 time-based 2FA tokens directly inside your device's hardware-encrypted Keystore. No cloud accounts, no sync leaks, zero network tracking.
StrongBox Keystore isolated
Standard HMAC-SHA1/256/512
No servers, no telemetry
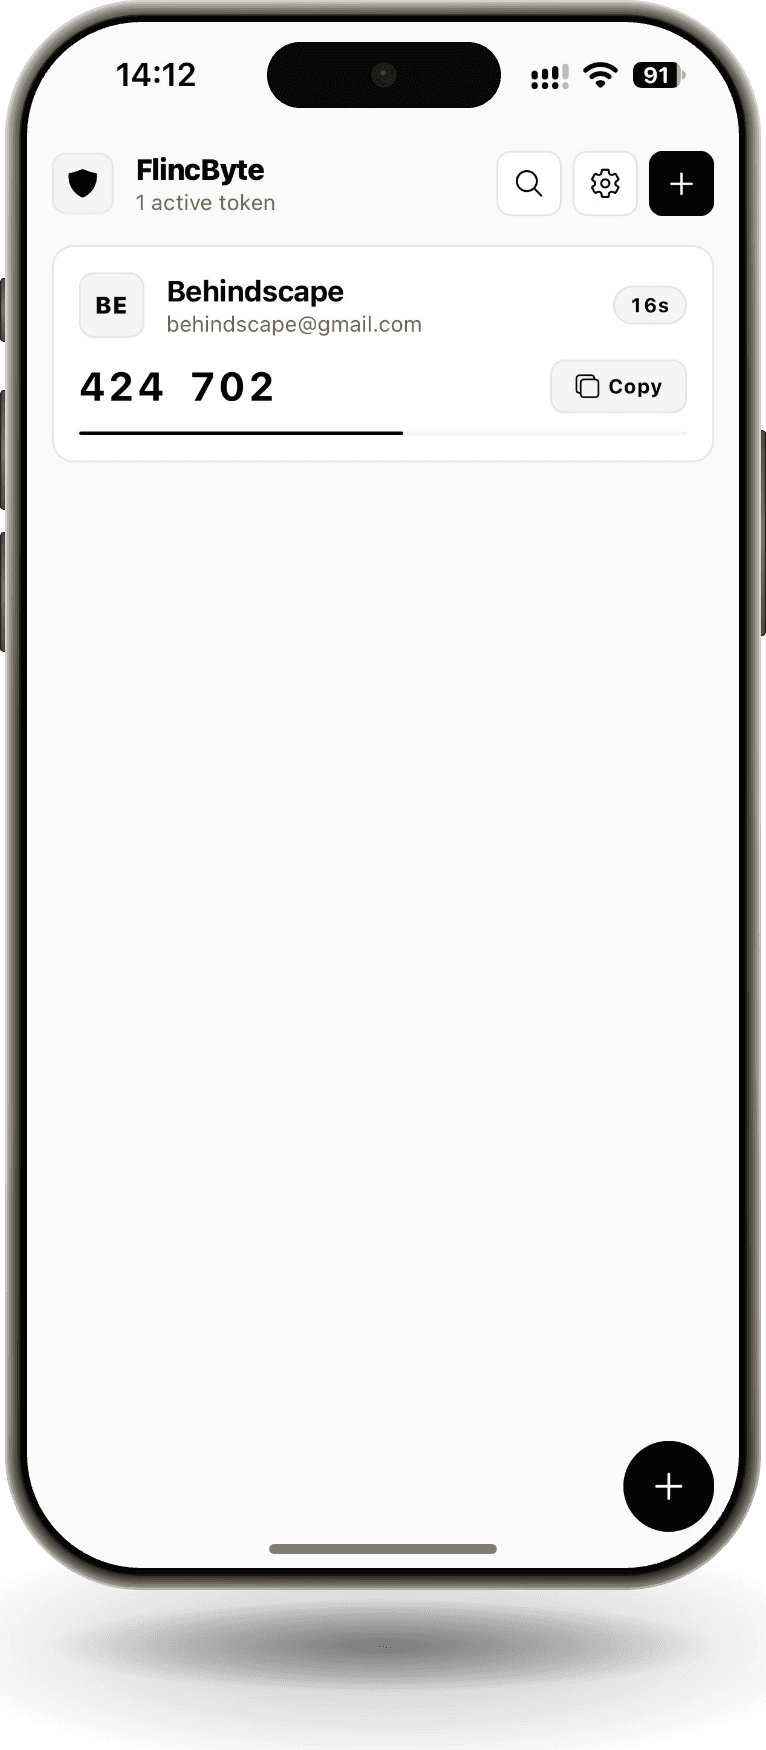
Experience the Engine in Real-Time
See how RFC 6238 time-synchronized HMAC generation works on-device. Switch accounts or customize key parameters instantly.
Behindscape Cloud
behindscape@gmail.com
One-Time Password Token
Cryptographic Parameters (RFC 6238 / RFC 4226)
Spaces and hyphens are sanitized automatically. Stored in StrongBox hardware.
T = floor(unix_timestamp / 30s) → HMAC-SHA1(Secret, T) → Truncate to 6 digits
Engineered with Precision & Restraint
Every screen is purpose-built following clean design foundations — zero clutter, rapid gesture response, and hardware-level privacy.
Live Token Dashboard
High-contrast monochrome cards with real-time countdown progress
Your 2FA tokens are presented with clean segmented typography, dynamic circular/linear countdown bars, issuer monograms, and one-tap copy with haptic feedback.
Defense-in-Depth Security
A privacy-first security model that replaces centralized cloud vulnerabilities with verifiable on-device hardware guarantees.
100% Offline by Architecture
FlincByte Authenticator declares zero internet permissions in its application manifest. It cannot connect to external servers, send telemetry, or leak cryptographic secrets because no network stack is attached.
StrongBox Keystore Encryption
Every imported 2FA secret is encrypted using AES-256-GCM and stored individually inside device hardware enclaves (StrongBox / TEE) restricted to unlocked device states.
RFC 6238 & RFC 4226 Engine
Built on pure mathematical specifications supporting HMAC-SHA1, HMAC-SHA256, HMAC-SHA512 with 6 or 8-digit outputs and flexible 30s or 60s periods.
Biometric Shield & Privacy Mask
Prevent shoulder-surfing and unauthorized physical access with instant biometric unlock (Fingerprint, Face Unlock) and app-switch privacy shielding.
Auto-Clearing Smart Clipboard
Copied 2FA codes are automatically wiped from system clipboard history after 15, 30, or 60 seconds to prevent background app snooping.
Why Local beats Cloud 2FA
Recent breaches have proven that storing 2FA keys in the cloud creates a catastrophic single point of failure. Here is how FlincByte Authenticator compares.
| Security & Architecture Matrix | FlincByte AuthenticatorZero-Knowledge | Google Authenticator | Microsoft Authenticator | Authy / Cloud 2FA |
|---|---|---|---|---|
Zero-Knowledge Offline Architecture No server connection or cloud sync required; zero network attack surface. | ||||
Zero Telemetry & Ad Trackers Zero diagnostic SDKs, advertising beacons, or analytics trackers. | ||||
No Account or Email Sign-in Required Use immediately upon install without tying 2FA secrets to an identity. | Optional | |||
Hardware StrongBox / TEE Keystore Isolation AES-256-GCM hardware-backed storage with device unlock restrictions. | Partial | Partial | ||
Auto-Clearing Smart Clipboard Purges copied authentication codes from memory after 15s, 30s, or 60s. | ||||
Biometric App Shield (Face / Fingerprint) Shields tokens behind biometric challenge with configurable timeouts. | ||||
Full HMAC-SHA1 / SHA256 / SHA512 Support Supports high-security SHA-256 and SHA-512 enterprise accounts. | SHA-1 Only | SHA-1 Only | ||
Backup Exclusion (android:allowBackup='false') Blocks unencrypted extraction via ADB or non-secure Google Drive backups. |
How Your 2FA Keys are Protected
A step-by-step overview of how credentials flow securely through device memory and hardware enclaves without ever touching the internet.
Zero-Trace Ingestion
Standard otpauth://totp/ QR codes or Base32 manual keys are parsed entirely in temporary memory. Spaces, hyphens, and padding are sanitized on-device without remote calls.
StrongBox Hardware Isolation
Each secret key is isolated in an individual encrypted slot inside device hardware secure storage (AES-256-GCM). Keychain accessibility is locked strictly to unlocked device states.
Deterministic Math Engine
Dynamic time intervals (T = unix_time / period) compute one-way HMAC hashes (SHA-1, SHA-256, SHA-512) adhering precisely to IETF RFC 6238 and RFC 4226 standards.
Volatile Memory Hygiene
Codes are displayed with monospaced clarity and copied to clipboard with automated self-destruct timers (15s, 30s, 60s), eliminating lingering memory traces.
Questions & Security Answers
Everything you need to know about FlincByte Authenticator's privacy model, encryption, and local operation.
Take Control of Your 2FA Security.
Download FlincByte Authenticator on Google Play. Zero tracking, zero cloud accounts, 100% offline hardware-encrypted security.